Cybersecurity conversations in schools tend to focus on the machinery: firewalls, servers, backups. But the most dangerous exposure in the school year has nothing to do with hardware. It is a stretch of time, and it is happening right now. Now that the opening rush is behind you and everyone assumes the hardest weeks are over, attention drifts, and that is exactly when your school is easiest to attack.
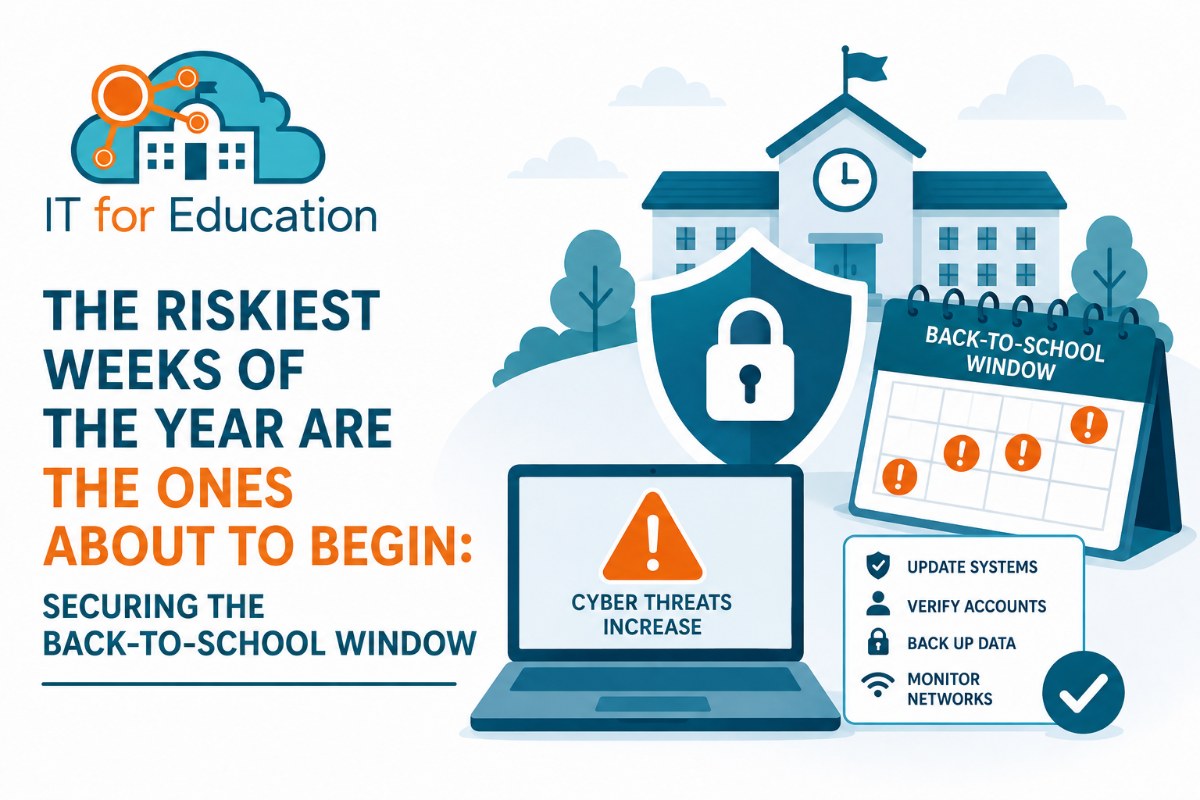
The reason is not a new threat. It is the season itself. Consider what the start of the year left behind. In the opening rush, a wave of new accounts was created for new hires and new students under deadline pressure, and many were never reviewed or fully locked down. Multi-factor authentication that got skipped in the scramble is often still skipped. Personal devices that reconnected in August are now moving freely on the network. And attackers, who know the school calendar as well as you do, keep sending their most convincing phishing all fall: an email that looks like it comes from the principal, the diocese, payroll, or a familiar vendor, arriving in a week when the early-year adrenaline has worn off and no one is looking twice.
For Catholic and Archdiocese schools, this exposure carries particular weight. Your school holds something families entrust to few institutions: their children’s records, their financial information, the details of a community that has believed in your school for generations. Across a multi-campus diocese, the exposure multiplies: every campus carrying the same loose ends from the opening weeks, every office onboarding at once, every staff member a potential door. A single compromised account can quietly reach far more than one classroom.
The internal weight of this is real. As a principal, president, or diocesan administrator, you are stewarding not only tuition dollars but the trust of parishioners and families who assume their information is safe with you. You did not take this role to spend your fall wondering whether the wire-transfer email your bookkeeper received was real, or whether the accounts created back in the opening weeks were ever locked down. And underneath it sits a quiet worry: that once the year settles into routine, a mistake is most likely, and least likely to be caught.
Here is the deeper truth. Good stewardship is not only protecting the building and the budget: it is protecting the community’s trust in the seasons it is most exposed. Your school exists to form students in faith and knowledge, not to play defense against a well-timed phishing email in the middle of a busy term. Security this time of year is less about technology than about people, accounts, and attention, and about having someone watching while your staff has their hands full teaching students.
This is exactly the gap IT for Education exists to close. For more than 24 years, we have worked exclusively with K-12 schools, and since 2002 we have partnered specifically with Florida’s Catholic and faith-based school communities across Miami-Dade, Broward, and Palm Beach. We understand both the technical reality of multi-campus environments and the stewardship responsibility that comes with serving a diocese. We are proud to be an MSP Titans in Education Award recipient, and we support thousands of students, teachers, and administrators across the region. You should not have to become an IT expert to keep your community’s trust safe, in the busy weeks and all year long.
With the year underway, we recommend three steps:
Schedule a Discovery Meeting: we learn about your school’s goals, current technology environment, and how accounts, access, and staff security are handled across every campus now that the year is underway.
Assess and Build a Roadmap: we identify where the human and identity risks live: dormant accounts, weak or missing multi-factor authentication, over-broad access, and the phishing patterns that target schools this time of year, and build a plan aligned to your budget and diocesan reporting.
Support, Secure, and Strategically Guide: we proactively monitor your environment through the fall and all year, so someone is watching for the suspicious login and the fraudulent email while your staff welcomes students.
Schools that close these gaps now move through the fall with locked-down accounts, staff who pause before they click, and a partner watching the door. Schools that don’t often learn where their exposure lives the hard way: on an ordinary week deep in the term, in front of families, when there is the least warning and the most trust at stake.
The risk didn’t leave when the first bell rang. Let’s make sure your school is protected through the weeks it’s most exposed, and all year.